Question: Can Magic Link authentication be used with a PWA, and can the login-link expiration be configured?
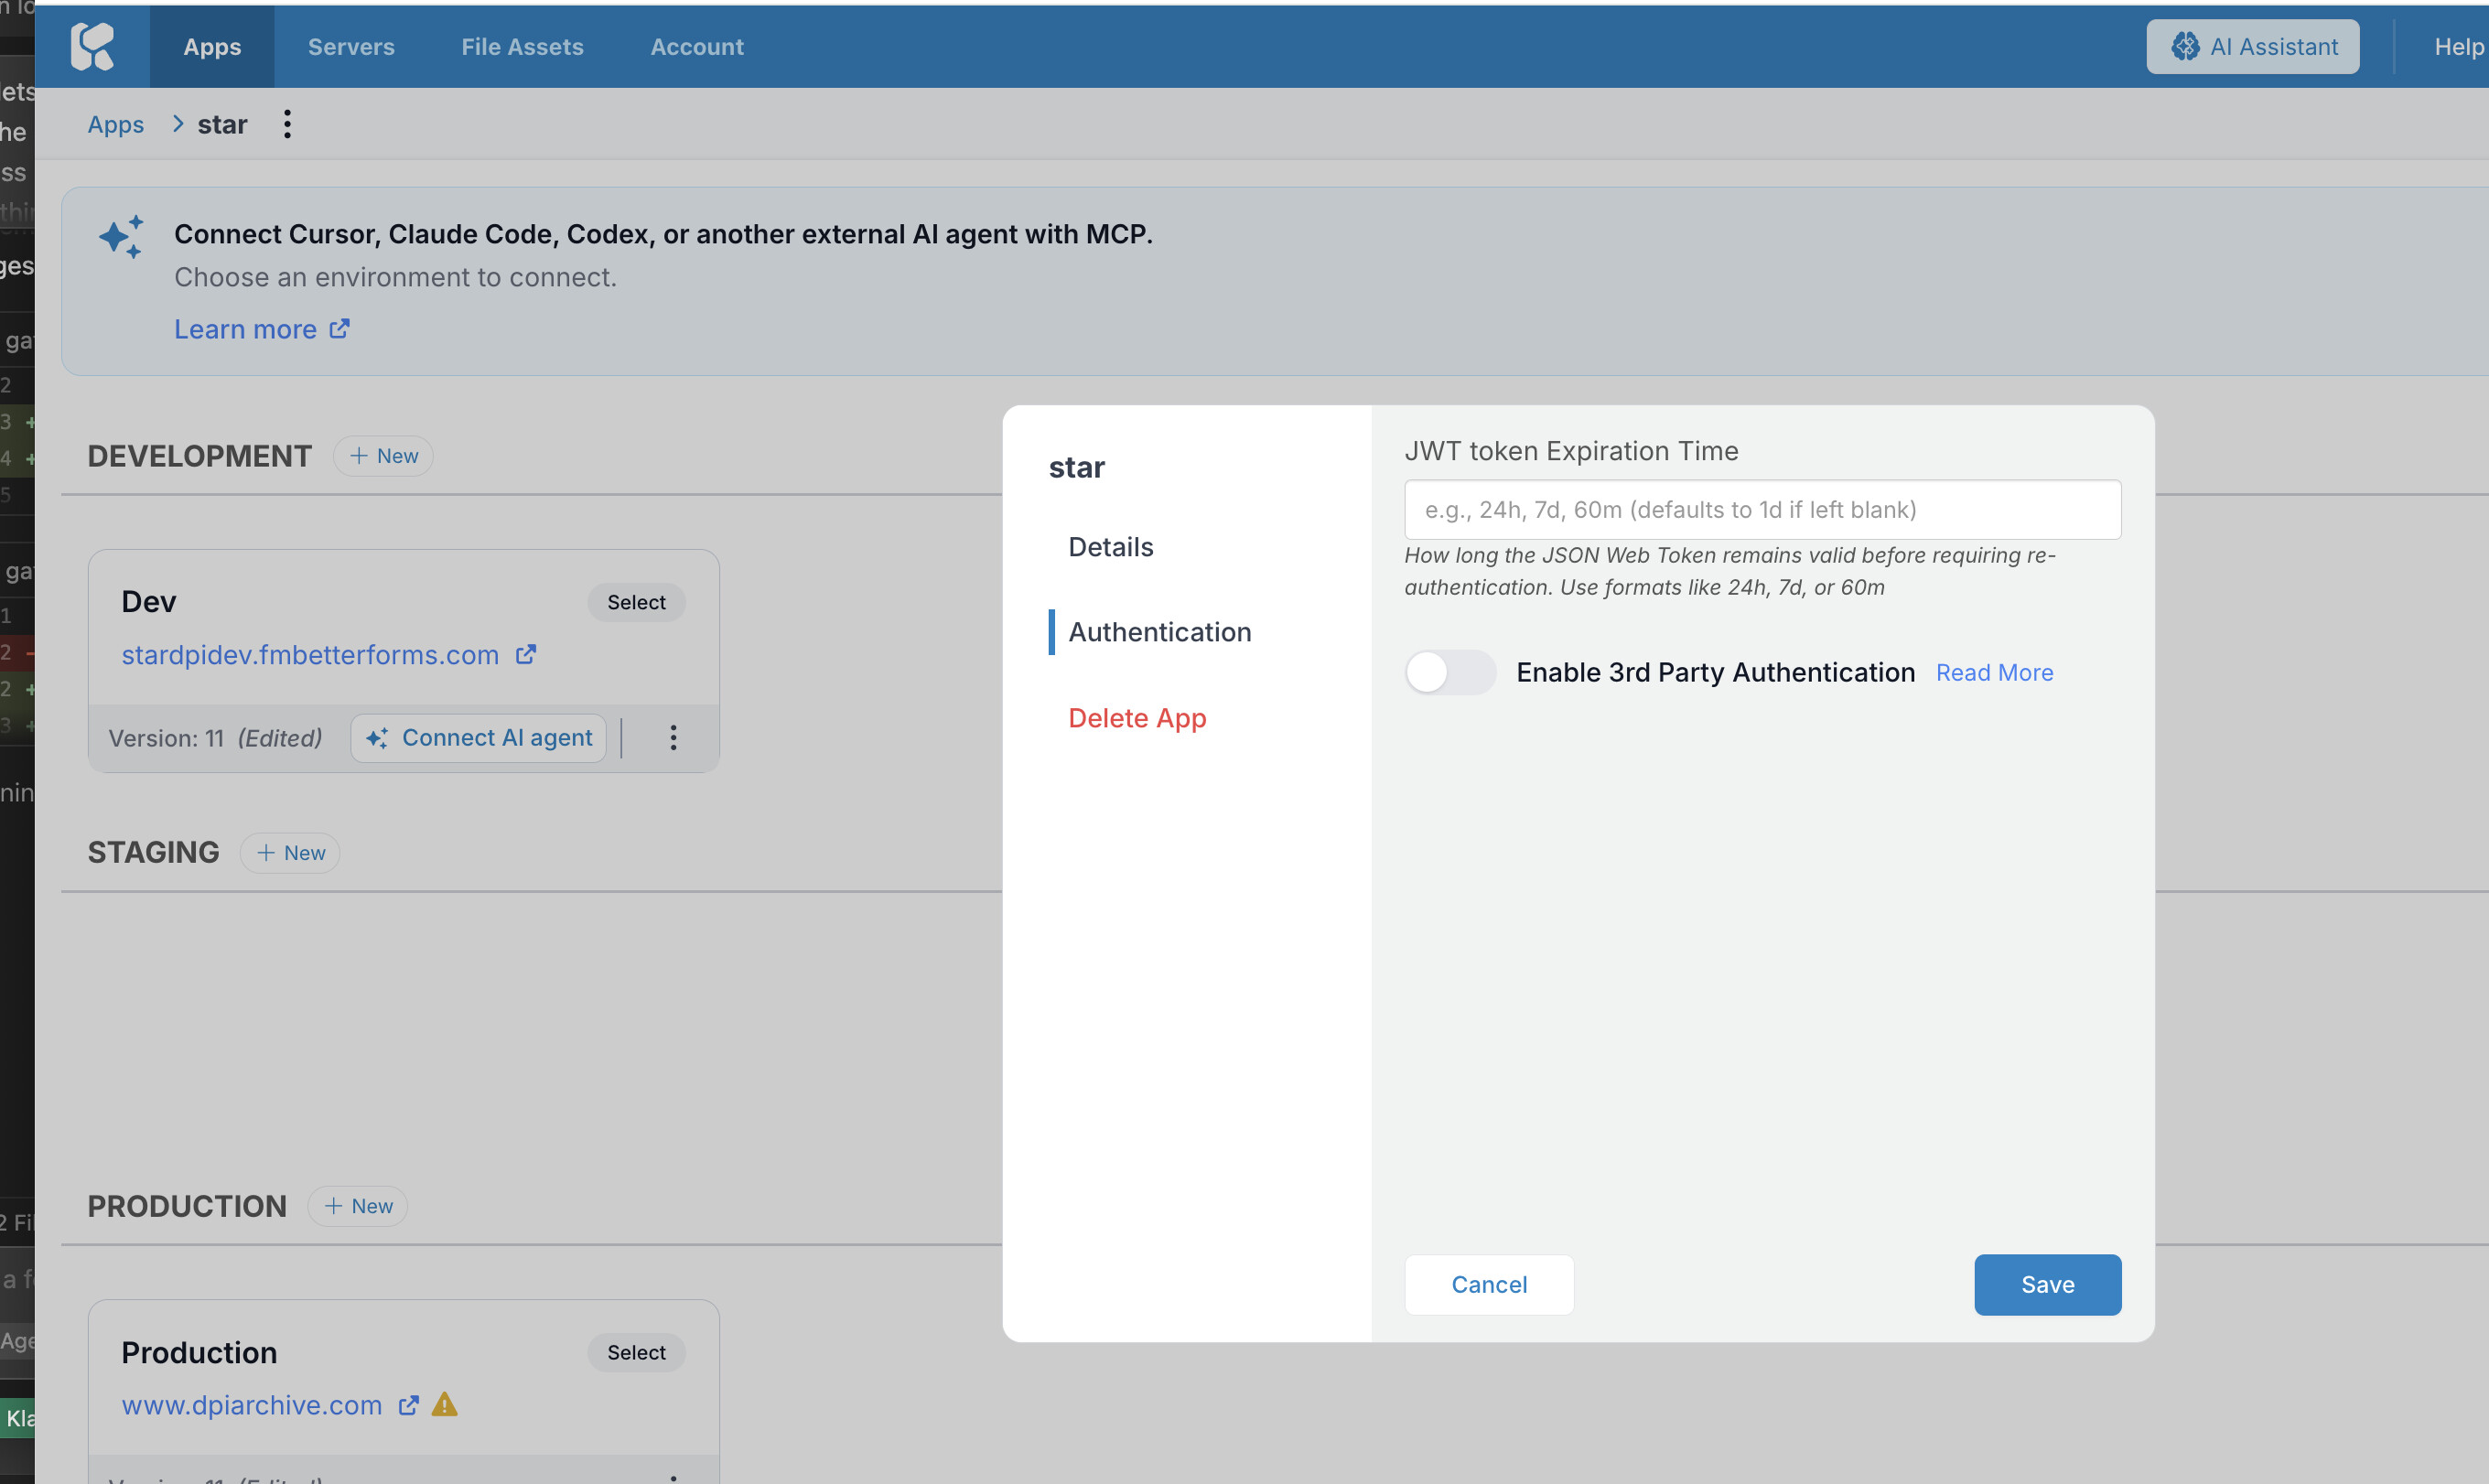
Answer: Yes. It should work fine with a PWA, and the token login expiration can be configured in the app’s Auth section—for example, to 10 days or 2 hours. For this use case, a longer expiration is typically appropriate.
Thread Attachments
Original Slack Thread
User URTFUJ1TP: I'm looking to implement Magic Link auth - any reason why that would be an issue with a PWA? I imagine it would work just fine but figured I'd check first
User UBBJX2EHM: yes hsould be fine, also you can control the token login expire policy from the app / auth section to eg: 10 days or 2 hours etc
User UBBJX2EHM: typically for that use case you woudl want it long
User URTFUJ1TP: that would be killer, users will love that. I always assumed that was managed on your servers.
User URTFUJ1TP: How would I implement exactly?
User UBBJX2EHM:
User UBBJX2EHM: top section
User URTFUJ1TP: Amazing. I can't keep up with all the new features you keep adding! :sweat_smile:
User URTFUJ1TP: Is this the correct action to request a magic link?

```{
                    "action": "authMagicRequest"
                },```
User URTFUJ1TP: I'm on v2.1.7 - not sure if v3 is needed?
User UBBJX2EHM: They are V3 only, unless you rolled your own somehow, see here:

<https://delfsengineering.notion.site/Authenticating-with-Magic-Links-32a66058a9ec80f58d16f6f1b412137c|delfsengineering.notion.site/Authenticati…>
User URTFUJ1TP: ...reading comprehension sure helps, doesn't it :joy:
User UBBJX2EHM: In fairness I just added the V3 note
User URTFUJ1TP: Ha, well I've been working in Klai for 18 hours straight so I'm not going to claim I'm at my most competent state right now either :rolling_on_the_floor_laughing:
User URTFUJ1TP: Ok, I've been avoiding v3 because JSON is familiar and comfortable - this is crazy intuitive, though. Extremely impressed!!